
Operating System
Data breaches cost companies millions annually—yet most vulnerabilities stem from internal gaps. These 10 proven internal safeguards empower cybersecurity leaders to fortify defenses, reduce human error risks, and align security with business operations.
Role-Based Access Control Implementation Guide
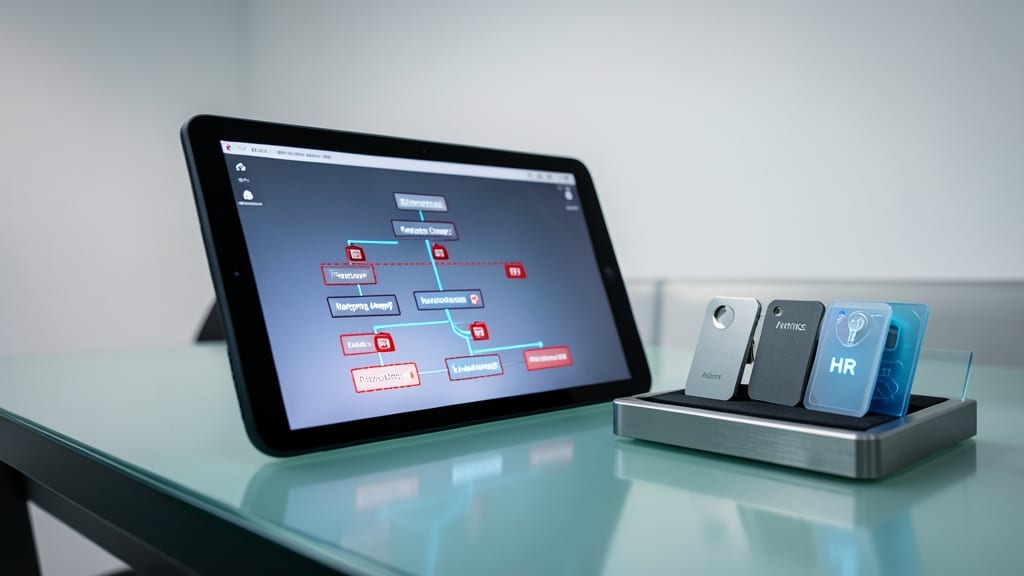
Tired of hearing about breaches caused by employees accessing data they shouldn’t? Role-Based Access Control (RBAC) solves this by tying permissions directly to job functions—no more "admin" accounts for everyone. It’s the digital equivalent of giving each employee a keycard that only opens the doors they need.
Modern RBAC systems like Microsoft Azure AD or Okta let you define granular roles (e.g., "HREmployeeRecords_ReadOnly") and enforce them across cloud and on-premises systems. Tools like OpenIAM even integrate with LDAP for legacy systems. The result? Employees get least-privilege access by default, cutting accidental leaks by up to 60% while stopping insider threats before they start.
This is your go-to safeguard if your company has departments with wildly different data needs—think finance vs. marketing vs. legal. Start with a role audit to map current access patterns, then automate enforcement with just-in-time privileges for temporary tasks. 💻
Automated Data Loss Prevention Solutions
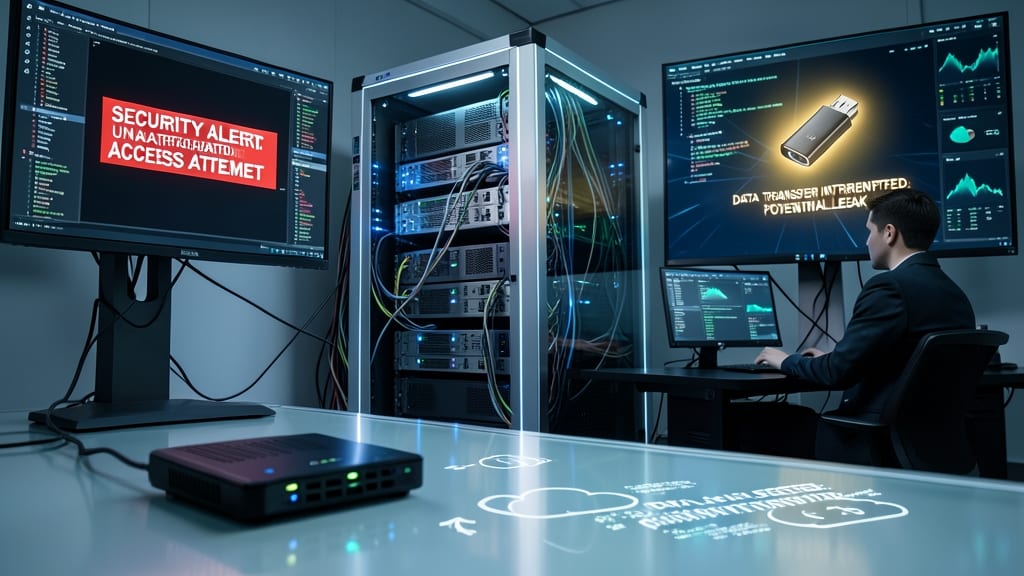
Forget hoping employees "won’t accidentally leak data"—modern automated Data Loss Prevention (DLP) solutions actively stop sensitive information from leaving your network. These AI-powered tools scan outgoing emails, cloud uploads, and even USB transfers in real-time, blocking transmissions that violate policies before they happen.
Leading solutions like Forcepoint DLP or Symantec DLP use machine learning to detect PHI (Protected Health Information), credit card numbers, or trade secrets—even in unstructured data. They integrate with Microsoft 365 and Google Workspace to monitor cloud activity, while policy templates for HIPAA, GDPR, or PCI DSS ensure compliance without manual audits. Some even provide forensic reports to trace how data was exposed.
Healthcare providers, financial firms, and legal offices see the biggest ROI, but any business handling confidential client data should prioritize this. The peace of mind from knowing sensitive files can’t walk out the door is worth the investment. 💡
Multi-Factor Authentication Enforcement Policy
Tired of relying solely on passwords that can be guessed, stolen, or phished? A Multi-Factor Authentication (MFA) Enforcement Policy adds an extra layer of protection by requiring a second verification step—whether it’s a fingerprint scan, hardware token, or push notification—before granting access to critical systems.
This policy forces users to authenticate via two or more factors (something they know, have, or are) before accessing sensitive data. For example, Microsoft Azure AD MFA integrates seamlessly with Active Directory, while Duo Security offers hardware tokens and mobile push notifications. Studies show MFA can block up to 99.9% of automated attacks, making it a non-negotiable safeguard for remote teams and finance departments handling high-value transactions. ⚡
Regular Security Awareness Training Programs
Your employees might be your biggest security risk—and your best defense. Security awareness training programs transform human error from liability to asset by using real-world phishing simulations that mirror actual attack vectors, not generic slideshows.
Look for platforms offering quarterly interactive modules with customizable scenarios (e.g., CEO fraud, invoice scams) and automated reporting to track individual progress against compliance benchmarks. The best programs integrate with your existing tools, like Microsoft 365 or Google Workspace, and provide certification tracking for audits. Studies show organizations using these programs see 70% fewer successful phishing attacks within six months.
This isn’t just for Fortune 500s—companies with frequent security incidents (even small teams) benefit most. Start with a phased rollout: begin with leadership, then expand to high-risk departments like finance or HR. 💡
Endpoint Detection and Response Systems
When employees connect personal devices to your network, Endpoint Detection and Response (EDR) systems act as silent sentinels—monitoring every endpoint for suspicious behavior before ransomware can lock your files. Unlike traditional antivirus, EDR uses AI-driven behavioral analysis to detect anomalies like unusual data exfiltration or lateral movement, stopping attacks in their tracks.
Modern EDR solutions like CrowdStrike Falcon or SentinelOne provide real-time threat hunting, automated response actions, and detailed forensic reports. They integrate with your existing security stack and work across Windows, macOS, and Linux, making them ideal for hybrid workforces. The key advantage? You get proactive protection without requiring employees to change their workflows.
Organizations with BYOD policies or distributed teams—especially in healthcare, finance, or legal—see the most value from EDR. It’s the difference between a minor alert and a full-blown breach. 💻
Secure File Sharing and Collaboration Tools
Tired of chasing down lost email attachments or worrying about sensitive files ending up in the wrong hands? Secure file-sharing platforms like Dropbox Business or Box replace risky attachments with end-to-end encryption and granular access controls—no IT degree required.
These tools offer automatic permission revocation (revoke access instantly if a contractor leaves), version history (restore files if edits go wrong), and large-file support**> (up to 50GB in a single upload). Creative teams love them for sharing high-res assets without clogging email servers.
Perfect for marketing agencies, design studios, or any team juggling large creative files—where security and collaboration need to coexist seamlessly. ✨
Network Segmentation Implementation Strategy
When a single compromised device could cripple your entire network, network segmentation acts as a digital firewall—dividing your infrastructure into isolated zones to stop breaches from spreading. Unlike traditional perimeter defenses, this strategy creates air gaps between departments, ensuring that if one area is breached, attackers can’t simply hop to your most sensitive systems.
Deploy VLANs (Virtual LANs) or micro-segmentation to separate environments like HR, finance, and R&D, with stateful firewalls controlling traffic between them. Tools like Cisco ACI or VMware NSX automate policy enforcement, while zero-trust principles ensure every access request is verified. For healthcare, HIPAA compliance requires patient data to reside in its own segmented zone with role-based firewall rules—limiting exposure even if other systems are compromised.
This approach is non-negotiable for power grids, hospitals, and financial institutions, where a single breach could mean life-or-death consequences. Start with your most critical assets—like patient records or SCADA systems—and expand segmentation gradually to create a layered defense. 🌟
Incident Response Playbook Development
When a breach happens, every second counts—but most organizations waste critical minutes scrambling for a response. An Incident Response Playbook turns chaos into action by outlining predefined containment, eradication, and recovery steps, slashing recovery time by 40% while meeting compliance deadlines like GDPR or HIPAA.
This isn’t just a document; it’s a battle-tested framework with escalation paths, communication templates, and forensic tools pre-configured. For example, a real-time breach simulation in the playbook might trigger automated network segmentation (like your earlier item) before human analysts intervene. The playbook also includes post-incident review checklists to identify root causes—like misconfigured access controls (see Item #1) or unpatched endpoints (Item #10).
Organizations in regulated industries (healthcare, finance) or those with public-facing data see the biggest ROI, but even SMBs benefit from the clarity it brings. Start with a NIST or ISO 27035-based template, then customize for your tech stack. 💪
Third-Party Risk Assessment Framework
Your company’s data isn’t just at risk from external hackers—it’s vulnerable through the backdoors of your vendors. A Third-Party Risk Assessment Framework evaluates third-party security before partnerships begin, blocking supply chain attacks before they start. This isn’t just another audit; it’s a proactive shield for organizations relying on contractors, cloud providers, or SaaS tools.
Look for frameworks that integrate automated compliance scoring (like NIST CSF or ISO 27001 alignment) and continuous monitoring to track vendor security posture. Tools like OneTrust Vendor Risk Management or Prevalent streamline assessments with real-time alerts for policy violations, while contractual SLAs enforce security obligations. The best frameworks also include penetration testing requirements for critical vendors—because no one should trust a vendor’s self-reported security.
This safeguard is non-negotiable for regulated industries (healthcare, finance) or any business with global contractor networks. Start with a pilot assessment of your top 10 vendors—you’ll likely uncover gaps you never knew existed. ✨
Continuous Vulnerability Scanning Schedule
Legacy systems often hide vulnerabilities like hidden termites—until it’s too late. A continuous vulnerability scanning schedule turns proactive defense into a weekly habit, using automated tools to detect and patch weaknesses before attackers even know they exist.
Most solutions like Nessus or OpenVAS run weekly scans with zero-configuration updates, flagging outdated software, misconfigured ports, and unpatched firmware. The key? Prioritizing fixes based on CVSS scores (Critical > High > Medium) and integrating results into your ticketing system for immediate action.
This isn’t just for Fortune 500s—smaller teams with older infrastructure (think pre-2015 servers or custom-built applications) see the biggest payoff. Set it, forget it, and sleep easier knowing your weak spots are getting patched before they become headlines. 💡